Archive: 2014

Networking1 min read

极路由绑定迅雷远程下载的另类方法

极路由可以通过安装云插件,成为一个迅雷远程下载的客户端。

但在绑定的过程中,由于极路由当前的设计思路,偶尔会出现无法正常绑定的情况。表现为在管理界面中显示出空白页,甚至直接显示出极路由公司首页。这些都导致无法将此路由绑定到迅雷。

如果碰到此类问题,可以通过这种方法绕开系统默认的绑定机制:

  1. 在内网的任何一台电脑上访问http://4006024680.com:9000/getsysinfo。如果你已经知道路由器的IP(默认为192.168.199.1),而且你的DNS未设置为默认,也可以直接使用路由器的IP地址代替4006024680.com的部分。浏览器会返回一行文字,其中一个引号中包括了6位英文和数字的组合。将其复制下,不包括引号。
  2. 访问迅雷远程下载网站http://yuancheng.xunlei.com。左侧上方找到添加按钮,输入复制的文字即可完成绑定。
  3. 之后就可以直接使用迅雷客户端或者迅雷的远程下载网站来分配任务了。并不需要在路由器中再进行绑定的操作。

Windows2 min read

Mixed Windows Authentication in IIS 8.5 (ASP.Net)

Update:

Actually, this not works. It looks OK because of the cache of client. There is no way to do this as I know.


Original:


I got a case recently to build a site in IIS 8.5:

  • When the visitor is logged on to the desktop with domain account, use this account for this website.
  • When the visitor is not using domain account, do not pop up a login window asking for domain account, redirecting to a version for anonymous instead.

I thought it's simple in IIS setting but I was wrong. The anonymous cannot work parallelly with Windows authentication.

After some digging in Google, I started my test:

  1. Deploy the site by using anonymous authentication.
  2. Select the login page for detecting domain user and change that page to Windows authentication instead of anonymous model.
  3. Add a custom page for this page on error 401. Model is set to "Execute a URL on this site".

It works good but...

When the login page opened, it should contain a Url as parameter for returning back to the original page. So I have to deal it in the customized 401 page. I turned that page to an ashx with the command context.Response.Redirect. The URL for returning can be cut from context.Request.RawUrl.

After that, it went wrong. Form the same server which has the IIS installed, it still works well. But when I try this page on another computer, it will always redirect to the anonymous version page no matter it's from the desktop logged with domain account or not. I'm sure that the site is added as Intranet zone and automatically logon is set in this zone.

Checked by network monitor, the browser will not get the 401 response in this scenario. As the ashx file request, only the 302 code is returned. That's the reason why the browser won't be notified to logon with the current user.

The solution is: if you want to use ashx with redirect function as a customized 401 page still, do not use context.Response.Redirect. Instead, try to do that with an HTML function with the 401 code in HTTP response.

context.Response.Status = "401 Unauthorized";
context.Response.StatusCode = 401;
context.Response.ContentType = "text/html";
context.Response.Write(@"<html>
<head>
<title>Redirecting</title>
<meta http-equiv=""refresh"" content=""0; url=" + redirectUrl + @""" />
");

It works like a charm.

I guess (yes, guess) when the browser get a 401 response first time, it will retry to the previous submitting/navigation with the domain account for login. If it's failed again, it will pop up a login window after the html page is displayed. So as I required in HTML code, after it navigate to another page, the browser has no chance to display the login window. That's the deal.

All I'm sure is it really works well. Hope it useful to you.

dotNet Product2 min read

A way to run nearly all functions of dotNet from SQL Server

Last night, I got a case to write a function in SQL Server 2005 to support the user account and password check against Active Directory. The user requirement is quite clear:

  • Create a scalar-valued function named LDAPUserCheck;
  • Parameter @username nvarchar(MAX) for user name to check;
  • Parameter @password nvarchar(MAX) for password matching the username specified;
  • Return bit 1 if succeeded, or 0 for all other reasons.

After a digging, I found that LDAP password authentication is not supported directly by SQL Server. But SQLCLR is a way to build the native dotnet program into SQL Server. In a new created SQLCLR project in VS 2005, I realized it's unable to add the reference System.DirectoryServices.AccountManagement, which is required by running the code for Active Directory authentication. But a Web Service is a choice.

My steps to achieve that:

1 Create and deploy a Web Service for the authentication check.

1.1 Create a Web Service project.

1.2 Add System.DirectoryServices.AccountManagement as a reference.

1.3 Add a setting DomainName as string for storing the domain name.

1.4 Add a service like this:

    public class LDAPAuthentication : System.Web.Services.WebService
    {
        static string domainName = Settings.Default.DomainName;

        [WebMethod]
        public bool Check(string userName, string password)
        {
            using (PrincipalContext pc = new PrincipalContext(ContextType.Domain, domainName))
            {
                // validate the credentials
                bool isValid = pc.ValidateCredentials(userName, password);
                return isValid;
            }
        }
    }

1.5 Deploy this service and use a application pool running by a domain user. This user should be added to IIS_WPG group in Windows Server 2003.

2 Create a SQLCLR project to call the Web Service.

2.1 Create a SQLCLR project in Visual Studio 2005.

2.2 Add a Web Service reference. It's named as LDAP in my project.

2.3 Add a User Defined Functions.

    [Microsoft.SqlServer.Server.SqlFunction]
    public static SqlBoolean LDAPUserCheck(
        SqlString username, SqlString password)
    {
        using (LDAPAuthentication.LDAP.LDAPAuthentication service = new LDAPAuthentication.LDAP.LDAPAuthentication())
        {
            if (service.Check(username.ToString(), password.ToString()))
            {
                return SqlBoolean.True;
            }
            else
            {
                return SqlBoolean.False;
            }
        }
    }

2.4 Set Permission Level to External in Database page of project setting.

2.5 Build this project to get the dll files. In my case, these files are named LDAPAuthentication.dll and LDAPAuthentication.XmlSerializers.dll.

3 Deploy this project into SQL Server 2005.

3.1 Enable the CLR support in SQL Server 2005 by running this code:

sp_configure 'show advanced options', 1;
GO
RECONFIGURE;
GO

sp_configure 'clr enabled', 1;
GO
RECONFIGURE;
GO

sp_configure 'show advanced options', 0;
GO
RECONFIGURE;
GO

3.2 Create a database for storing this function. Or, you can use any existed database as well. In my case, I created a database "tester".

3.3 Set trustworthy on this database by running:

ALTER DATABASE [tester] SET trustworthy ON

3.4 Copy the 2 dll files created in step 2 to this server. In my case, these are stored in C:\SQLCLR folder.

3.5 Create assemblies in SQL Server by running:

create assembly [LDAPAuthentication] from 'C:\SQLCLR\LDAPAuthentication.dll' with permission_set = external_access
create assembly [LDAPAuthentication.XmlSerializers] from 'C:\SQLCLR\LDAPAuthentication.XmlSerializers.dll' with permission_set = external_access

3.6 Create function to run the method we've created in VS 2005:

CREATE FUNCTION [dbo].[LDAPUserCheck](@username [nvarchar](4000), @password [nvarchar](4000))
RETURNS [bit] WITH EXECUTE AS CALLER
AS 
EXTERNAL NAME [LDAPAuthentication].[UserDefinedFunctions].[LDAPUserCheck]

Now everything is done. You can call this function like all others created by SQL. Run this for test.

select dbo.LDAPUserCheck('myusername','mypassword')
 

Networking1 min read

Testing ZeroShell in enterprise

Hi.

ZeroShell 3 is launched recently, including many new features. I was a fan of this router software for several years and it works like a charm in my Net5501. Now I'm trying to introduce it to the company which I work for.

I deploy this software twice in my company. One is for a virtualization desktops, powered by QoS. This is quite necessary for a network which contains more than 100 clients for internet accessing.

Another one is for all mobiles and pads, powered by Captive Portal. But this function doesn't work like predicted. Mobiles which joined this network by AP will not pop up a login page automatically. In some restaurants and hotels, after a device joined a network, a web page will be pop up automatically for login, but this function is still missing in this release of ZeroShell.

One more defect is about DHCP server. User defined options are not supported yet.


Apple Stuff1 min read

Reset LaunchPad in OSX Yosemite

In OSX Yosemite, the way for resetting LaunchPad has been changed.

New command is:
defaults write com.apple.dock ResetLaunchPad -bool true; killall Dock

Warning: By resetting LaunchPad, all settings related to LaunchPad will be removed like position of icons and groups.

Gossip1 min read

程序员的TOP25句话


「老帖转发,非原创」

  1. 尽管不能运行,但感觉怎么样?
  2. 你的机器中可能有病毒吧!
  3. 肯定有人改了我的代码。
  4. 程序可以运行,但是没被测试过。
  5. 已经做好了,还没测试。
  6. 我不是已经改了吗?
  7. 这个怎么能做呢?
  8. 我不可能测试每一项啊!
  9. 正巧给碰上了错!
  10. 根本就没时间做。
  11. 当然我还得修改。
  12. 差不多了!
  13. 哦,这不过是一个功能。
  14. 你肯定操作错了。
  15. 是是,一定及时/按时完成。
  16. 我没动过那个模块!
  17. 你的测试数据有问题。
  18. 那个用户又犯错了。
  19. 操作系统升级了吗?
  20. 这台机器好象有问题。
  21. 这怎么可能!
  22. 恩,程序还需要一些修改。
  23. 昨天还好好的,......
  24. 我从来没听过......
  25. 奇怪......

Gossip4 min read

一次精彩的网络约架(锤子手机)

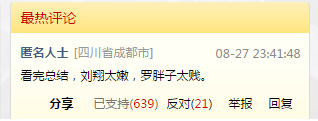
对于王自如与罗永浩的网络视频约架,本我没留意。8月27日当晚好多人谈论,约我关注一下,于是我大概的看了一下之前的视频,并完整看了那个居然也可以拿来直播的约架。如果一句话可以评论,我想我终于找到了广电总局的价值。

其实,从王接受了罗的“邀请”就已经输了,而且输的非常彻底。既然是准备来吵架的,就要按吵架去准备呀。

首先,如果真的罗确信王做了不该做的事情,那么这事情就不会发生在北京的某个演播室,而是应该在深圳的某个审判庭。虽然罗的公司也面临着由于各种负面报道产生的财务问题,不过来趟深圳应该不是什么问题,或许王以及雷也愿意给他报销差旅费呢。

在网络直播的过程中,强烈感受到的是录音棚出身的王,绝对始终完全的不是课堂出身的罗的对手,不论从应变能力和心理把控上,那是输到车尾灯都看不到了。当然,我不能排除王是一个优秀的演员的可能性,但至少演技一流。

王在演说上的弱势,是完全可以预估的。毕竟没有受过常年的演讲培训。这点不仅观众知道,王和罗也应该是完全可以预估的。但王的准备还是有很多问题。

  1. 既然接受了罗的约架,就应该准备好,罗绝对不会谈任何技术上的问题。技术上的问题是实打实的,这问题只能在律师取整和审判庭上进行。现实约架比的是体力,网络约架比的是应变力和口才。在打架的时候讲道理,您这真的是来捧哏的。
  2. 既然不谈技术问题,那王就应该知道,罗会使用一个中国人最善用的逻辑来进行攻击,即,如果我无法在事实证据上驳倒你,我就揣测你的动机;如果动机上还是找不到确切证据,那我就攻击你的人品。王显然是没有对这些东西做应对的材料准备和口头演练,被罗打到毫无还口之力。
  3. 既然已经提前知道了自己视频确实有问题,为何不事先公布勘误呢。

当然,王的评测视频中,确实存在不少问题。但问题应按事实认定还是评论分析,分别讨论。

  1. 在背板开关问题上,事实认定错误,王也完成了道歉。但罗在此事确实有理。
  2. 在海绵贴纸问题上,事实认定是它阻隔了散热,评论分析王有明显的引导观众,使其认为是设计缺陷。但评论分析是没有所谓对错之分的。就如同买了一份报纸,里面的事实描述是正确的,但是评论则是报纸的观点。这份媒体又不是强制收看,评论没有所谓的强加性。这也正是罗没有办法启用法律途径的原因。
  3. 在石墨贴纸问题上,事实认定错误。虽然手机散热差是事实,但把石墨贴纸空隙当做散热的原因是不对的。可惜王没有把握到这个问题的本质,在约架的时候被罗抓住攻击这个点,而忽略了它存在的原因——散热问题。
  4. 在色彩还原设备测试上,事实认定错误。错误的使用了测试工具,得出的数据并不代表有效感官。
  5. 在屏幕可视角测试上,存在疏忽。虽然我们不知道是否是有意为之,不过这样做确实加剧了效果。在测试媒体上,这种行为是不够严谨的。

罗的本次约架(我不认为是对质,虽然它后面准备了大字版是这样说),虽然想到了为了演讲效果准备大字版,但却没有准备纸笔,当然也许正是有意为之。为了企业,放弃自己的名誉,作为企业家也无可厚非。感谢你告诉我王的咨询服务做的没有职业道德,我们可以绕开它;感谢你告诉我王的手机备件是灰色的,我可以不去修手机。你没谈视频中的事实认定问题是怎样?这样好像你就不是来对质视频问题的了吧,果然是来约架的吗?

当一个人开始问候你家人的时候,你就知道他已经没理了。当一个人开始讨论你的动机和人品的时候,说明你做的这事多少还是靠谱的。

给王一个技术的建议(绝非人生的忠告):如果你不打算去吵架,就别去。如果你一定要去,至少学学周总理在万隆会议的发言“我们不是来吵架的”,然后再听到泼妇骂街的时候,你只需要呵呵就行了。

最后引用cnbeta的最热评论: